If Liquibase is Git, then Bytebase is GitHub/GitLab.
Bytebase and Liquibase both handle database schema migration, but the right choice depends on how your team ships database changes — not just which databases you run. A solo developer writing changelogs in a terminal has different needs than a platform team where DBAs review every production migration.
How They Approach Schema Migration
Liquibase (v5.0.4, August 2026) is a CLI-first migration engine. You define changes in XML, YAML, SQL, or JSON changelogs, then run liquibase update to apply them. It slots into any CI/CD pipeline as a command-line step. The commercial edition — rebranded from "Liquibase Pro" to Liquibase Secure in September 2025 — adds policy checks, flow files for workflow automation, and structured JSON logging.
Bytebase (v3.22, August 2026) is a web-based platform where developers submit changes, DBAs review them, and the system rolls out across environments. Schema migration is one part of it — SQL review, access control, data masking, and audit logging are built in.
Put another way: Liquibase is Git for databases; Bytebase is GitHub/GitLab for databases.
What They Have in Common
- Native SQL support for defining schema changes.
- GitOps integration — trigger migrations from pull requests.
- Schema synchronization and diff capabilities.
- Change history tracking.
- Tiered pricing with a free community edition.
- Both are open source — though Liquibase switched from Apache 2.0 to the Functional Source License (FSL) in September 2025 with v5.0. Bytebase is MIT licensed, with enterprise features under a commercial license.
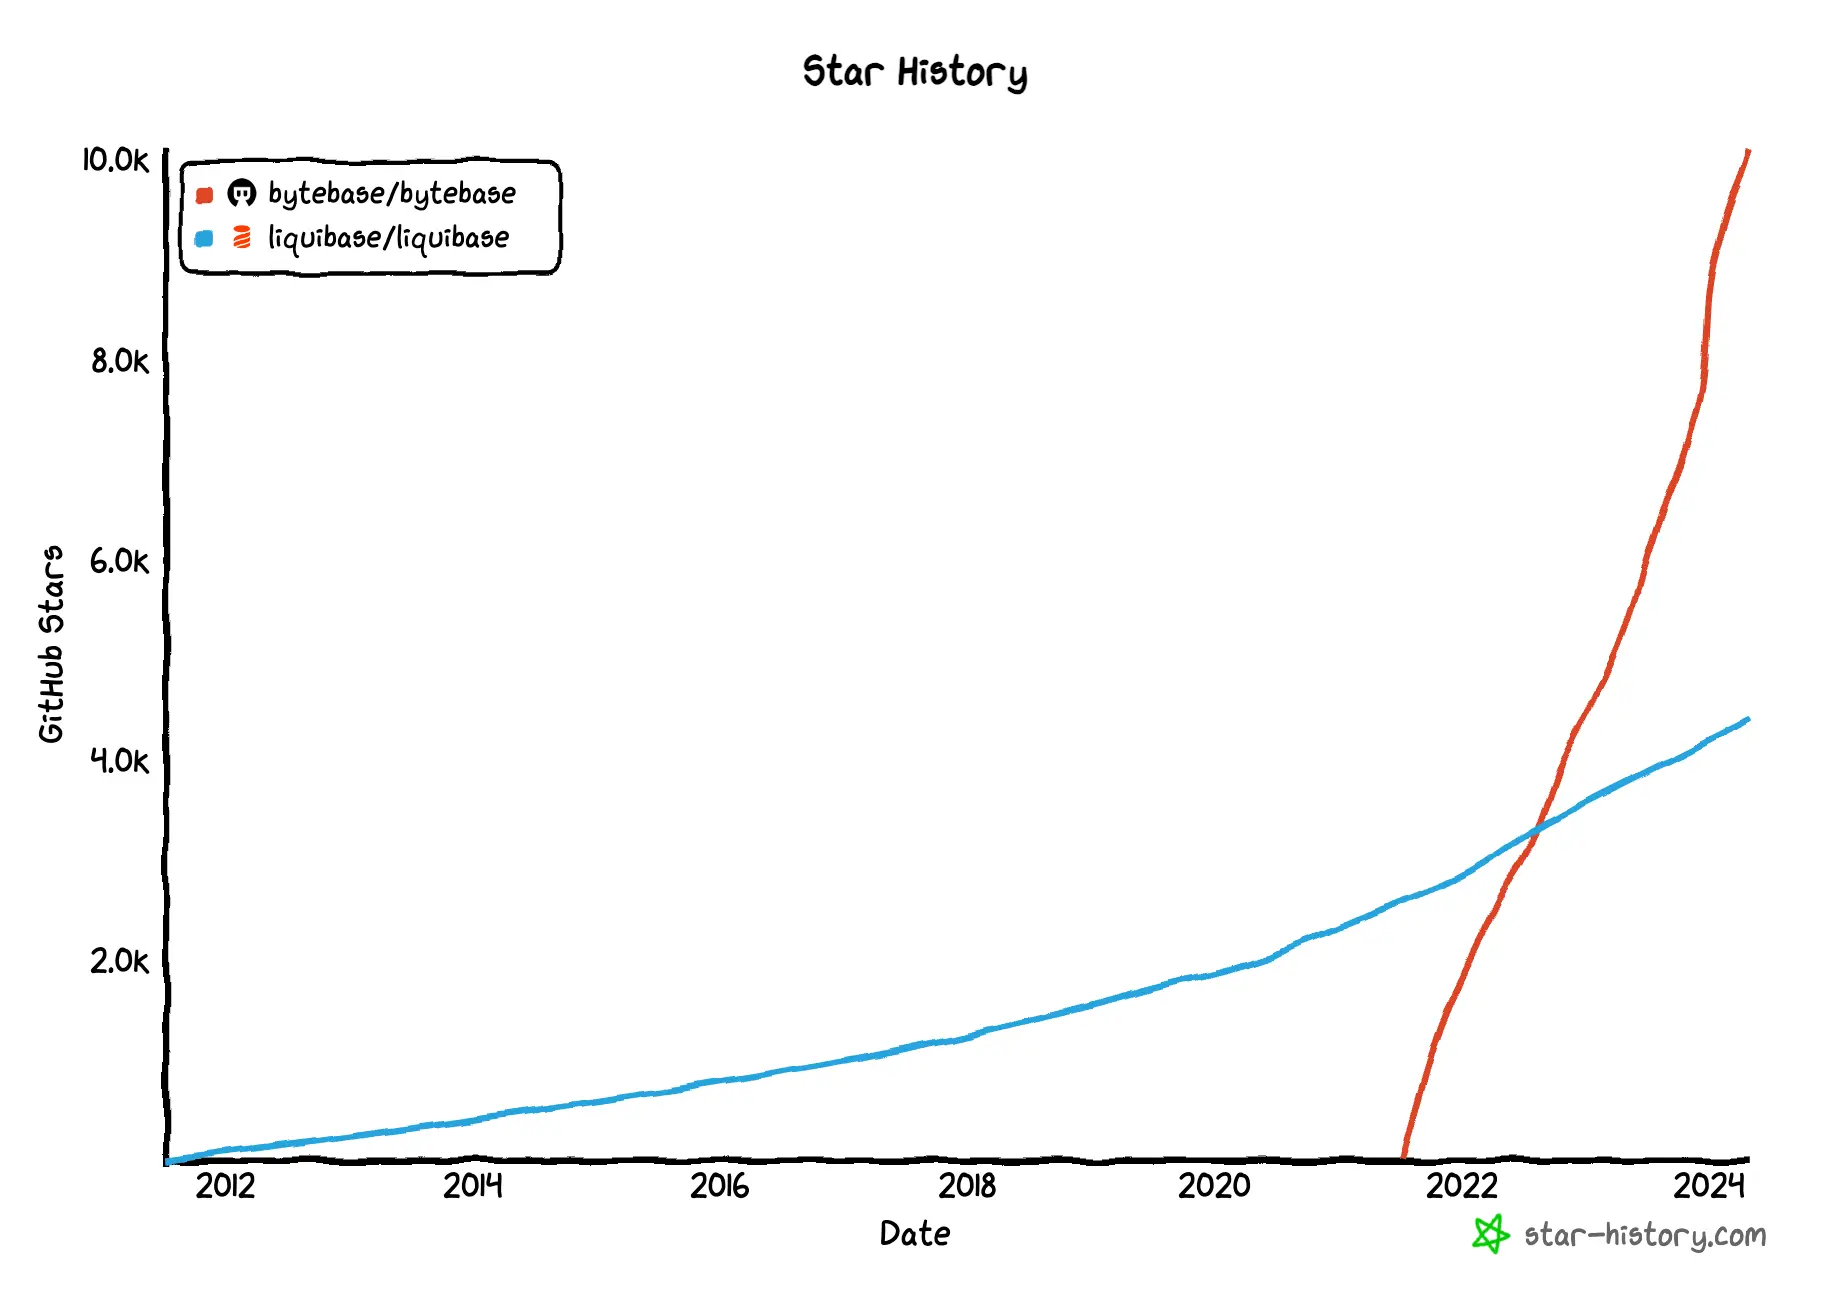 Star history of Bytebase and Liquibase
Key Differences Between Bytebase and Liquibase
| Liquibase | Bytebase | |
|---|---|---|
| Developer interface | CLI; Secure adds VS Code extension | Web GUI + API + Terraform provider |
| Supported databases | 60+ | 23 |
| Installation | Java 17 + JVM | Single Go binary, Docker, or K8s |
| Change execution | Changelog + CLI; Secure adds Flow files | Issue-based GUI or GitOps |
| Declarative schema (SDL) | — (migration-based by design) | PostgreSQL, MySQL (beta), all tiers |
| Schema sync | liquibase diff + diff-changelog (CLI, 1-to-1) | GUI-based batch sync (1-to-many) |
| Batch change | Manual scripting; Secure adds Flow files | Multi-environment on all tiers; multi-tenant database groups on Pro and Enterprise |
| SQL review / policy checks | Secure only: policy checks (custom rules) | 200+ rules (all tiers) |
| Approval flow | — | All tiers: per-environment rollout permissions; Enterprise: risk-based custom approval |
| Rollback | Basic (manual scripts); Secure: granular + automated | Data: backup + one-click rollback; schema: roll back to an earlier version; all tiers |
| CI/CD integration | Any CLI-based pipeline; Secure adds Flow files | GitOps (GitHub, GitLab, Bitbucket, Azure DevOps) + API |
| Change history | DATABASECHANGELOG table; Secure adds structured JSON logging | GUI with diff view + issue linkage |
| Security and compliance | Secure: policy checks (incl. PII detection), drift detection, vault integrations, structured logs; no runtime data access controls | SQL review on all tiers; Enterprise: risk-based approval, JIT access, data masking; audit log on Pro and Enterprise |
| Database access control & audit | — | All tiers: workspace/project roles; Pro: SSO, 7-day audit log; Enterprise: + dynamic data masking, custom roles, just-in-time data access, unlimited audit log |
| Pricing | Community: free (FSL); Secure: quote-based (5 tiers) | Community: free (MIT); Pro: public per-user pricing; Enterprise: custom |
Developer Interface
Liquibase is CLI-only for the Community edition. After Liquibase Hub was sunset in April 2023, there is no web dashboard. The Secure edition added a VS Code extension ("Liquibase Secure Developer") for IDE-based interaction, but the primary workflow remains the terminal.
Bytebase provides a web-based GUI where developers submit changes, DBAs review them, and the platform handles rollout. It also exposes a full API, a Terraform provider for infrastructure-as-code workflows, and GitOps workflow tutorials for Git-driven automation.
Supported Databases
Liquibase supports 60+ databases through a modular extension system. Core databases include PostgreSQL, MySQL, Oracle, SQL Server, MariaDB, Snowflake, MongoDB, and DB2. Many database extensions are community-contributed.
Bytebase supports 23 database engines with deep integration: 9 RDBMS (MySQL, PostgreSQL, Oracle, SQL Server, MariaDB, TiDB, OceanBase, CockroachDB, Spanner), 6 NoSQL (MongoDB, Redis, Cassandra, DocumentDB, DynamoDB, Cosmos DB), 7 data warehouses (Snowflake, BigQuery, Redshift, Hive, ClickHouse, Databricks, StarRocks), and Elasticsearch.
Liquibase covers more databases. Bytebase goes deeper on each one it supports — online schema change for MySQL, engine-specific SQL review rules for PostgreSQL, column-level data masking that understands each database's type system.
Installation
Liquibase requires Java 17+ (as of v5.0). Install the JVM, then install Liquibase. The Secure edition includes a one-step certified installer with bundled database drivers.
Bytebase ships as a single Go binary with no external dependencies. Deploy via Docker or Kubernetes in under 5 minutes.
Change Execution
Liquibase uses changelogs — files in XML, YAML, SQL, or JSON that define database changes. You run liquibase update to apply them. Changelogs support preconditions (skip a changeset if the table already exists), contexts (apply only in certain environments), and labels (tag changesets for selective execution). The Secure edition adds Flow files: reusable YAML-based pipelines that chain multiple Liquibase commands with conditional logic — for example, run validate first, then update, and only run rollback if update fails.
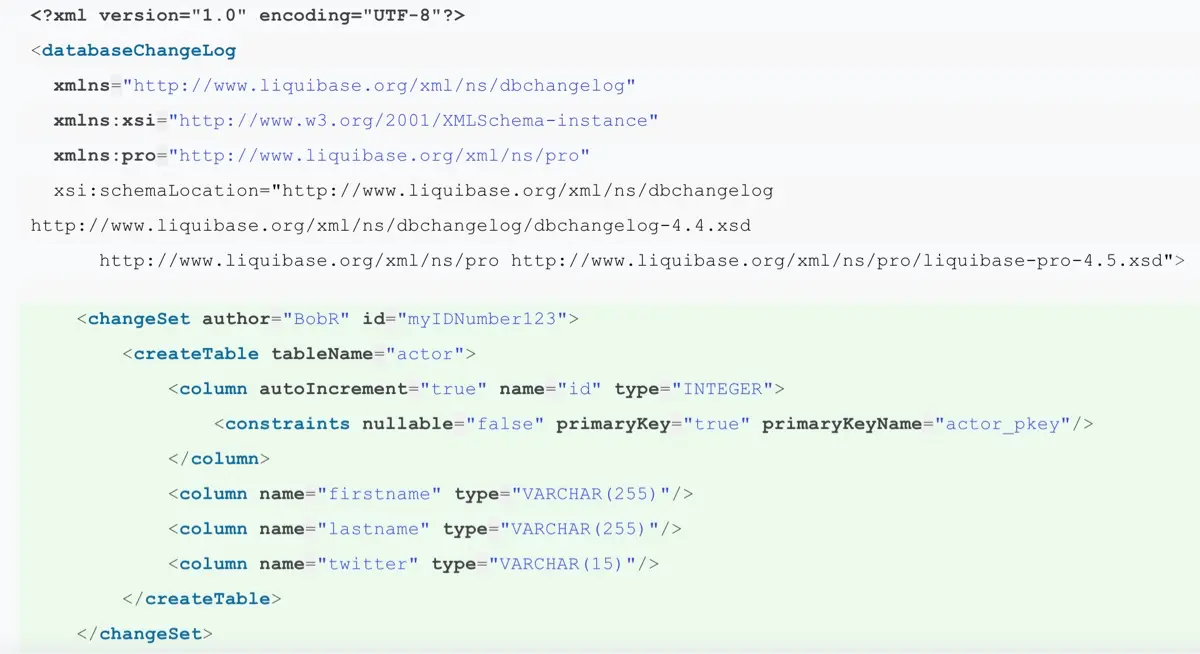 Liquibase changelog definition
Bytebase uses an issue-based workflow. A developer creates an issue containing SQL statements, which goes through SQL review, and any approval flow that applies, before execution. Issues can target a single database or batch across environments. Bytebase also supports online schema change for MySQL with gh-ost — large tables stay writable during the migration instead of being locked for its duration.
Declarative Schema Management
The two tools take different positions on where your schema lives.
Liquibase is migration-based by design. The changelog is the source of truth: you append a changeset for every alteration, and the database's state is whatever the accumulated changesets produced. liquibase diff-changelog (see Schema sync) narrows the gap, but its output is still an ordered list of changesets you version and apply. There is no mode where you hand Liquibase a target schema and let it reconcile.
Bytebase supports both models. Versioned migration works the way you would expect. Alongside it, the state-based workflow lets you declare the target schema in your repo, and Bytebase computes the migration DDL to reach it. The generated DDL still passes through SQL review and the same rollout controls as a hand-written change, so declaring a target does not mean skipping the gates.
Know the scope before you plan around it. State-based migration covers PostgreSQL and MySQL (5.7 and 8.0) only, with MySQL in beta as of 3.21; SQL Server, Oracle, and MongoDB use versioned migration. Within those two engines it handles a defined set of object types rather than arbitrary SQL: tables, indexes, views, and functions on both, plus sequences on PostgreSQL and procedures, triggers, and events on MySQL. PostgreSQL triggers and complex stored procedures are not covered, and DML stays out of scope on both. The limitations page is the current list. It is available on every tier, including Community.
Schema Sync
Liquibase offers liquibase diff to compare two databases and liquibase diff-changelog to generate a changelog from the differences. Both are CLI commands — you specify a reference database and a target, and Liquibase outputs the structural differences or the changesets needed to bring the target in line.
Bytebase has a built-in schema sync through the GUI. Pick a source database and one or more targets — Bytebase generates the DDL diff for each and applies them as a batch change issue, going through SQL review and the same rollout controls as any other change. Useful for keeping staging in sync with prod, or syncing schema across dozens of tenant databases at once.
Batch Change
Liquibase doesn't have built-in multi-environment orchestration. You run liquibase update against each target database separately in your CI/CD pipeline. The Secure edition's Flow files help — you can define a YAML pipeline that runs the same changelog against dev, staging, and prod in sequence, with gates between stages. But it's still you writing the orchestration, not the tool managing it.
Bytebase handles this natively. A single issue can roll out changes across multiple environments (dev → staging → prod) on every tier. Rolling out across multiple tenants uses database groups, available on Pro and Enterprise.
SQL Review and Policy Checks
Liquibase Community has no built-in SQL quality checks. Liquibase Secure offers Policy Checks (renamed from "Quality Checks" in September 2024) with custom rules and conditional logic chains (AND/OR/NOT). You can write checks like "block any changeset that drops a table in production" or "require a rollback section for every changeset." Checks run against changelogs, SQL, and the live database, can be written in Python or regex, and set an exit code by severity so a CI pipeline can block on them. Secure 5.1 added a check that flags personal or health data in INSERT and UPDATE statements. These operate on changelog structure and SQL patterns — useful for governance, though less granular than engine-specific SQL analysis.
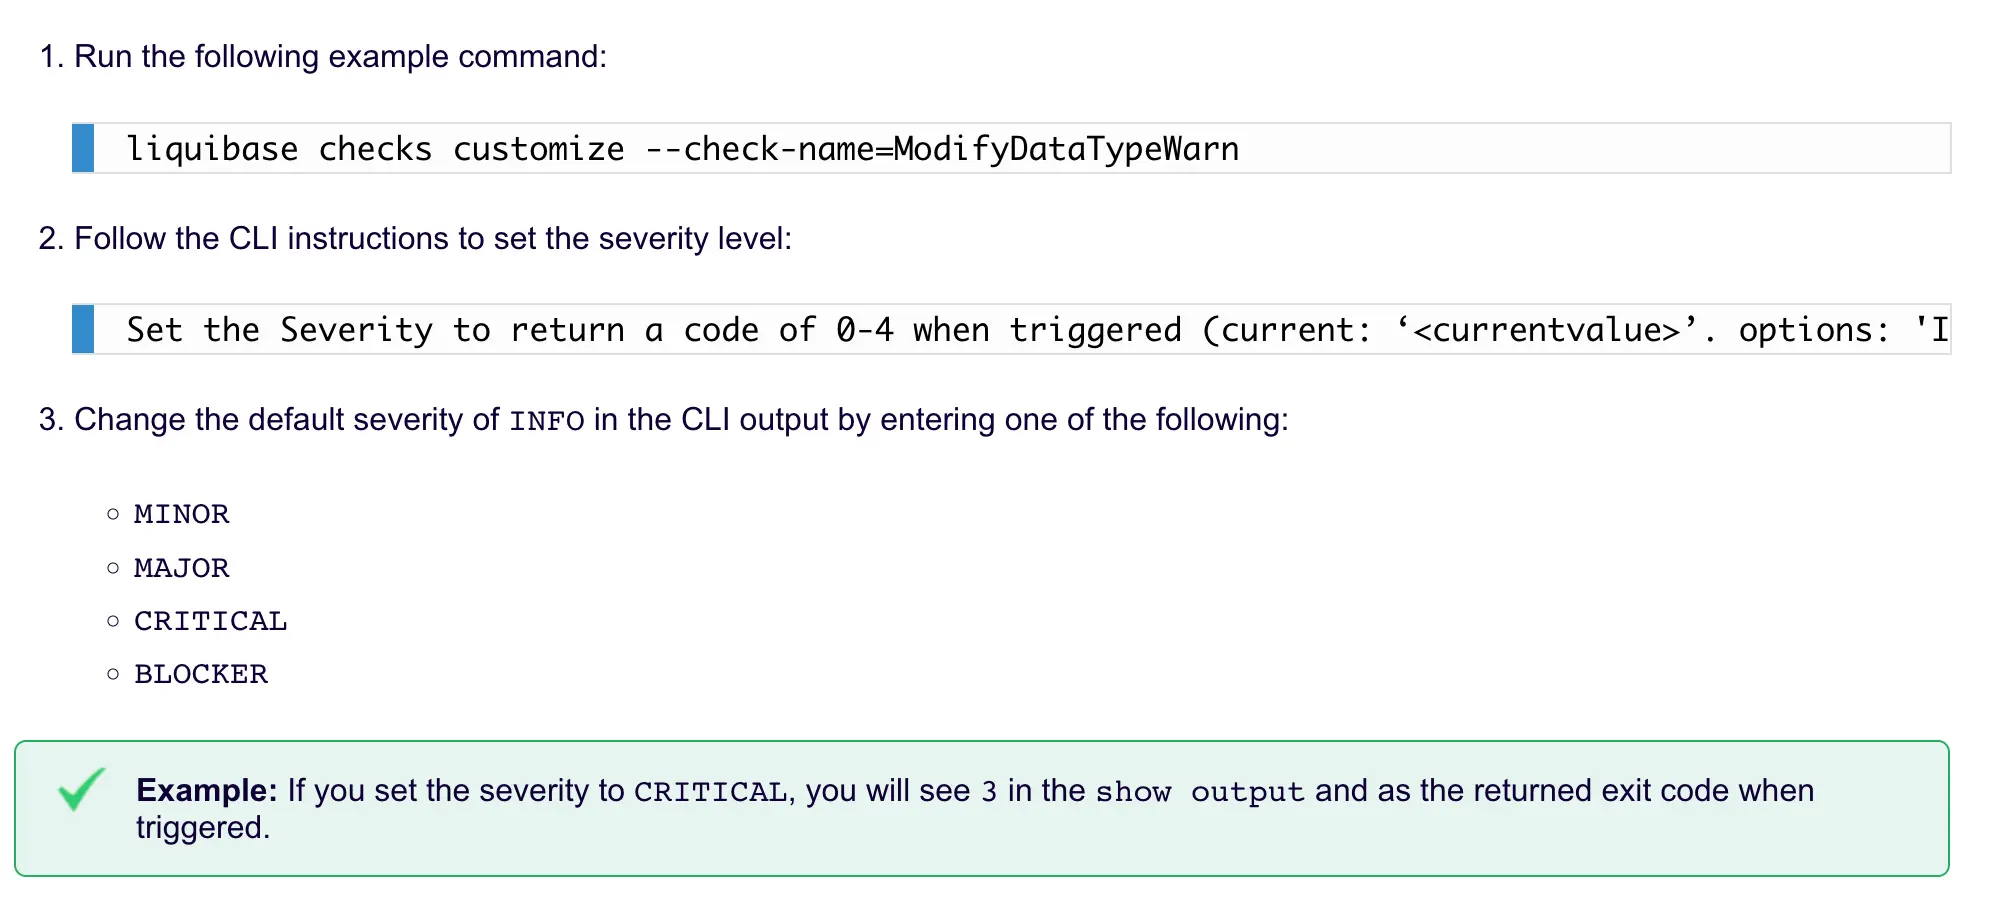 Liquibase policy check configuration
Bytebase includes SQL Review with 200+ rules across MySQL, PostgreSQL, Oracle, SQL Server, and more — available in the free tier. Rules are database-engine-specific (not generic), and you can configure error levels per environment (warn in dev, block in prod).
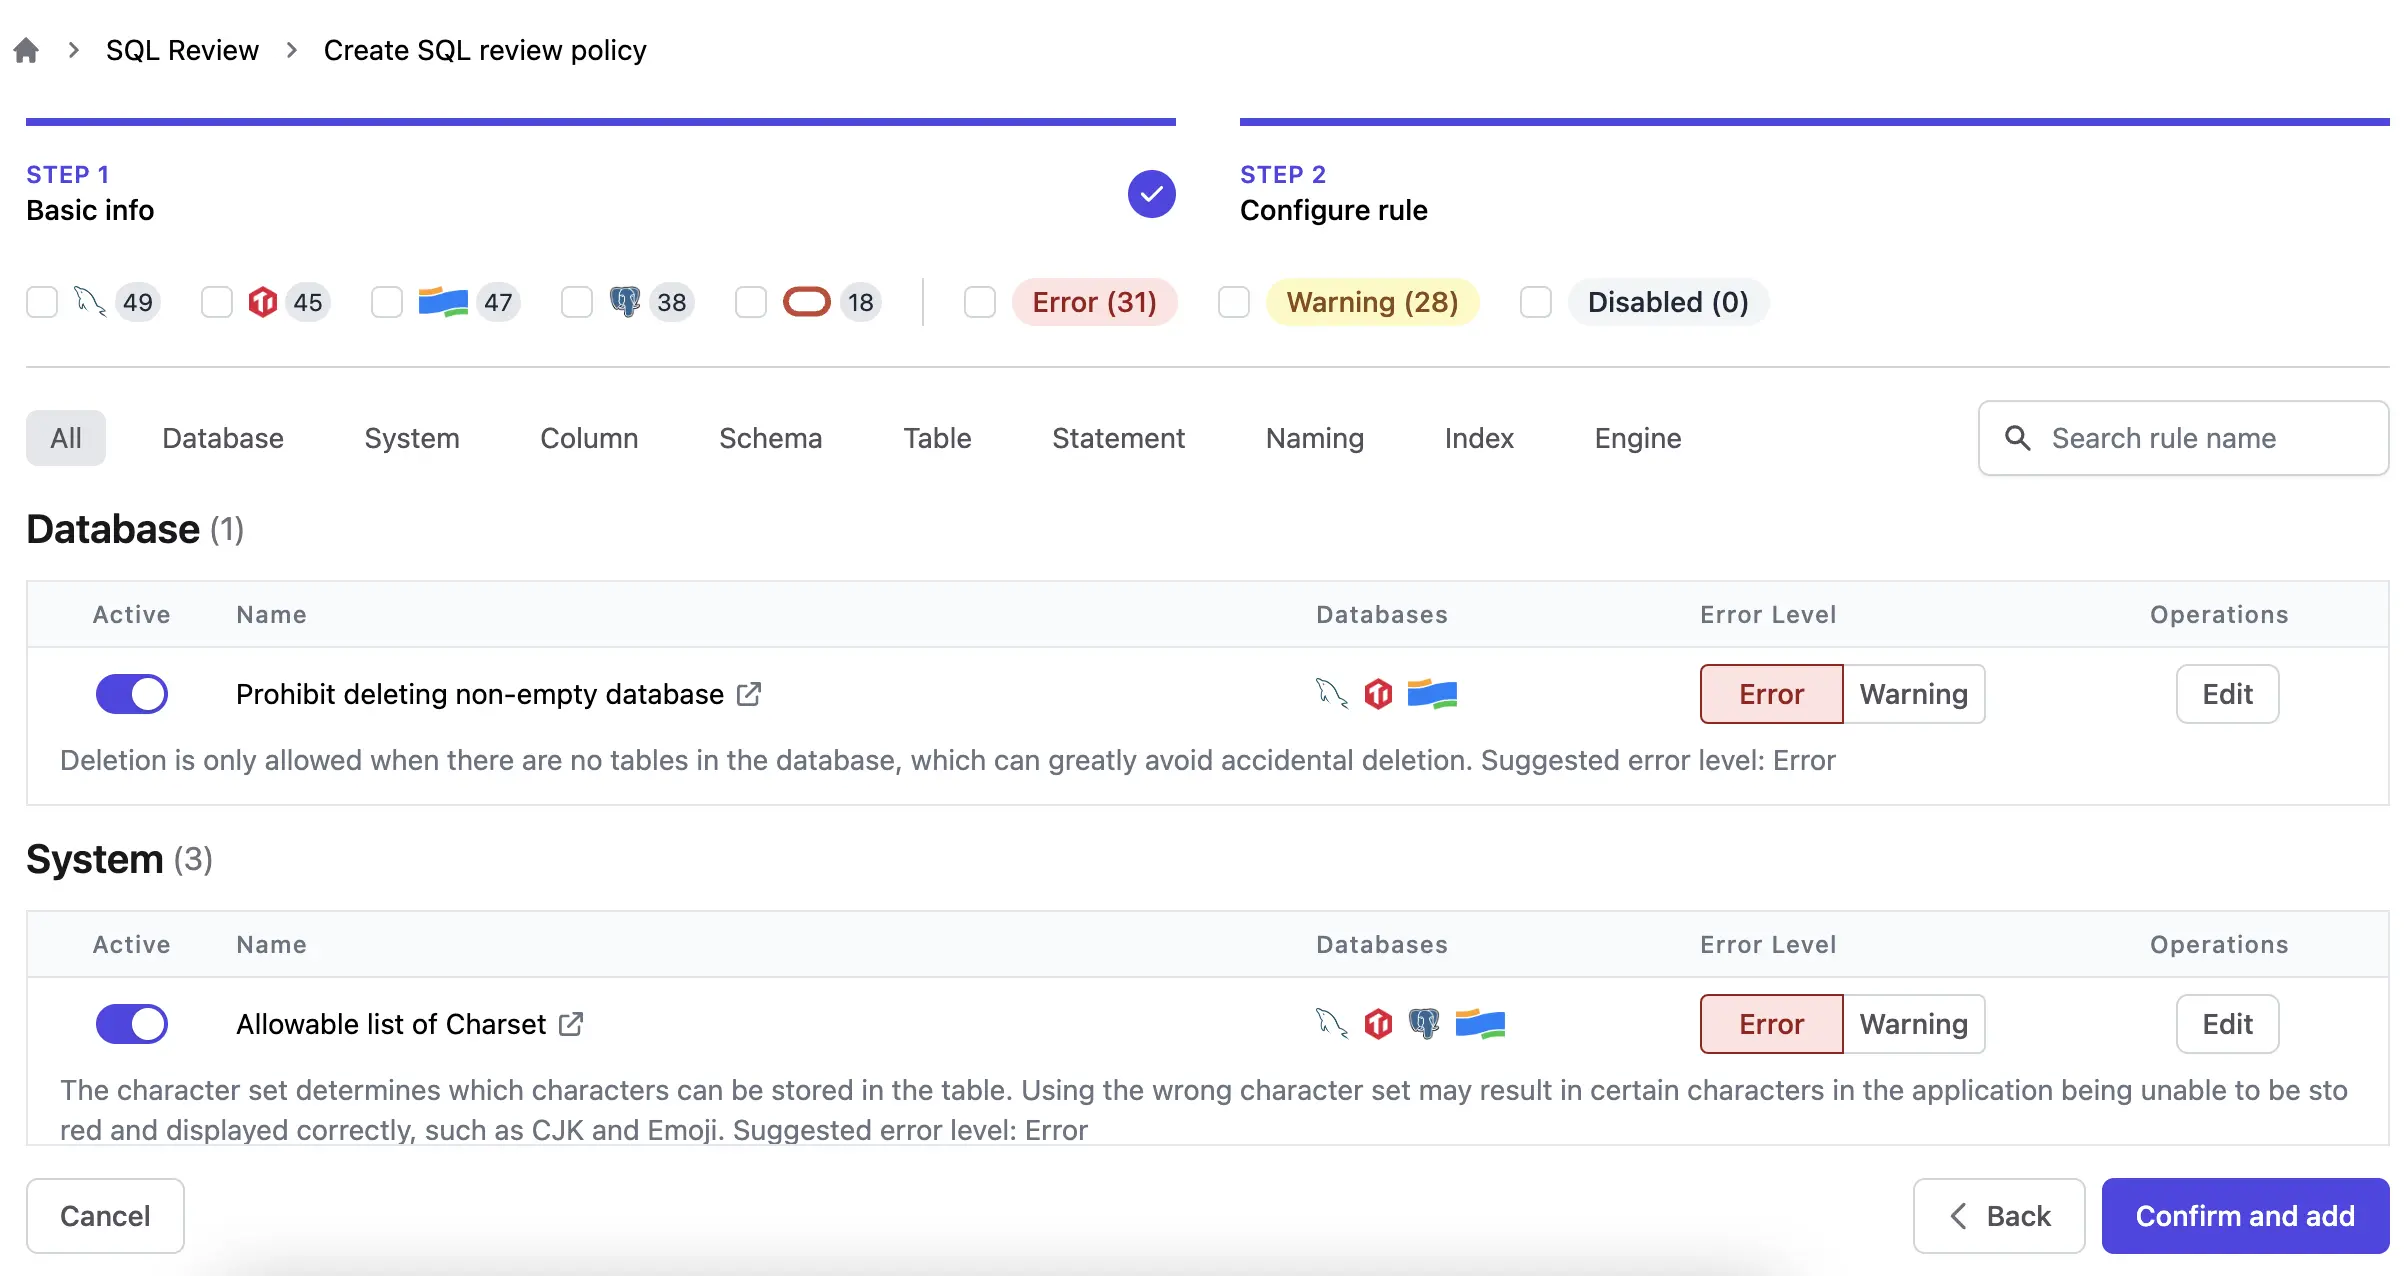 Bytebase SQL review rules configuration
SQL review triggers automatically in two places:
- When a change issue is created.
- In GitOps — when a new PR containing SQL is created.
Approval Flow
Liquibase has no built-in approval workflow in either edition. Approval happens outside the tool — in your CI/CD pipeline, Jira tickets, or Slack messages. Liquibase's own compliance guides describe approvals as enforced through CI/CD and SSO, and its announced Deployment Connectors (ServiceNow among them, rolling out from fall 2026) route changes through existing change-management systems.
Bytebase Community and Pro use rollout policies: you control who may deploy to each environment and whether plan checks must pass first, but there is no approval workflow. Bytebase Enterprise adds custom approval flows. Each flow has a condition built from the environment, project, database engine, SQL type, affected rows, and a risk level Bytebase calculates from the statement type, so you can write rules like "DDL on production needs DBA approval" or "an UPDATE affecting more than 1,000 rows needs a second reviewer." The same flows cover role requests and just-in-time data access, not only schema changes.
Custom approval applies to changes made in Bytebase. In a GitOps workflow, the approval happens in the pull request instead, with SQL review running as a required check.
Rollback
Liquibase Community supports basic rollback — you write rollback SQL manually in your changelog and run liquibase rollback to a specific tag or date. Liquibase Secure improves this with auto-generated rollback scripts for common operations, rollback reports (added in v4.27.0) that show what was rolled back, skipped, or failed, and custom rollback logic for complex cases.
Bytebase handles data and schema separately, on every tier. For data changes, it backs up the affected rows before an UPDATE or DELETE runs and offers one-click rollback from that backup, on MySQL, PostgreSQL, Oracle, and SQL Server. For schema changes, you roll back from a changelog entry or sync the database back to an earlier schema version. No manual rollback scripts needed.
CI/CD Integration
Liquibase fits into any CI/CD pipeline as a CLI step — GitHub Actions, GitLab CI, Jenkins, CircleCI. The Secure edition's Flow files add reusable pipeline definitions with conditional branching based on exit codes.
Bytebase offers GitOps setup with GitHub, GitLab, Bitbucket, and Azure DevOps. SQL review runs in your CI as a merge check, and merged SQL files become a release that Bytebase rolls out across environments. For other platforms, Bytebase's API lets you wire up any CI/CD pipeline.
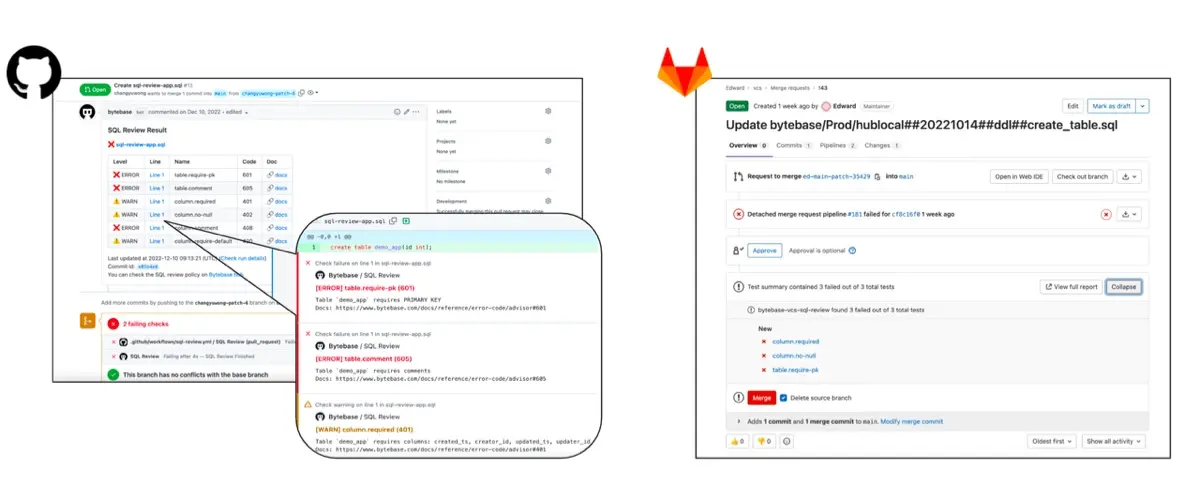 Bytebase GitOps SQL review in GitLab merge request
Change History
Liquibase tracks changes in the DATABASECHANGELOG table — a record of which changesets were applied, when, and by whom. You query it directly with SQL. The Secure edition adds structured JSON logging (replacing the old text-based logs) that you can pipe into Datadog, Splunk, or any log aggregator. This is how Liquibase replaced the Hub dashboard — instead of a built-in UI, you build observability from the log stream.
Bytebase provides a visual change history with schema diffs and links back to the originating issue.
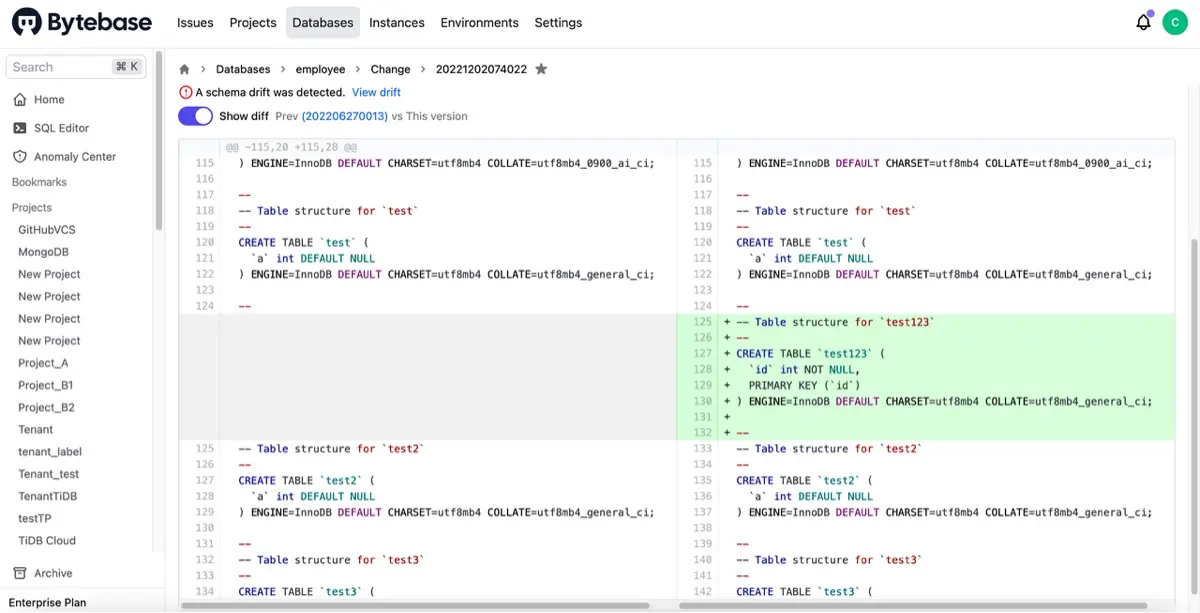 Bytebase change history with diff view
Database Access Control and Audit
Liquibase governs schema changes, not access to data. Neither edition controls who can query production, masks data, or grants temporary access; Liquibase positions itself at the schema layer and leaves runtime access to other tools. On the audit side, Community records applied changesets in the DATABASECHANGELOG table, and Secure adds structured JSON logs and operation reports that you ship to a SIEM. Those tell you what changed and when, but not who queried what data. If you need database access governance, you'd pair Liquibase with a separate tool.
Bytebase layers access control across its tiers:
- Community — workspace and project roles (Owner, DBA, Developer) with built-in permissions, plus SQL Editor for controlled query access.
- Pro — adds SSO (Google and GitHub), user groups, and an audit log with 7-day retention.
- Enterprise — custom roles with granular permissions, dynamic data masking at column level, enterprise SSO (OIDC, OAuth 2.0, LDAP), 2FA, SCIM, an audit log with no retention limit, and just-in-time data access — developers request temporary query access, a reviewer approves it, and access expires automatically.
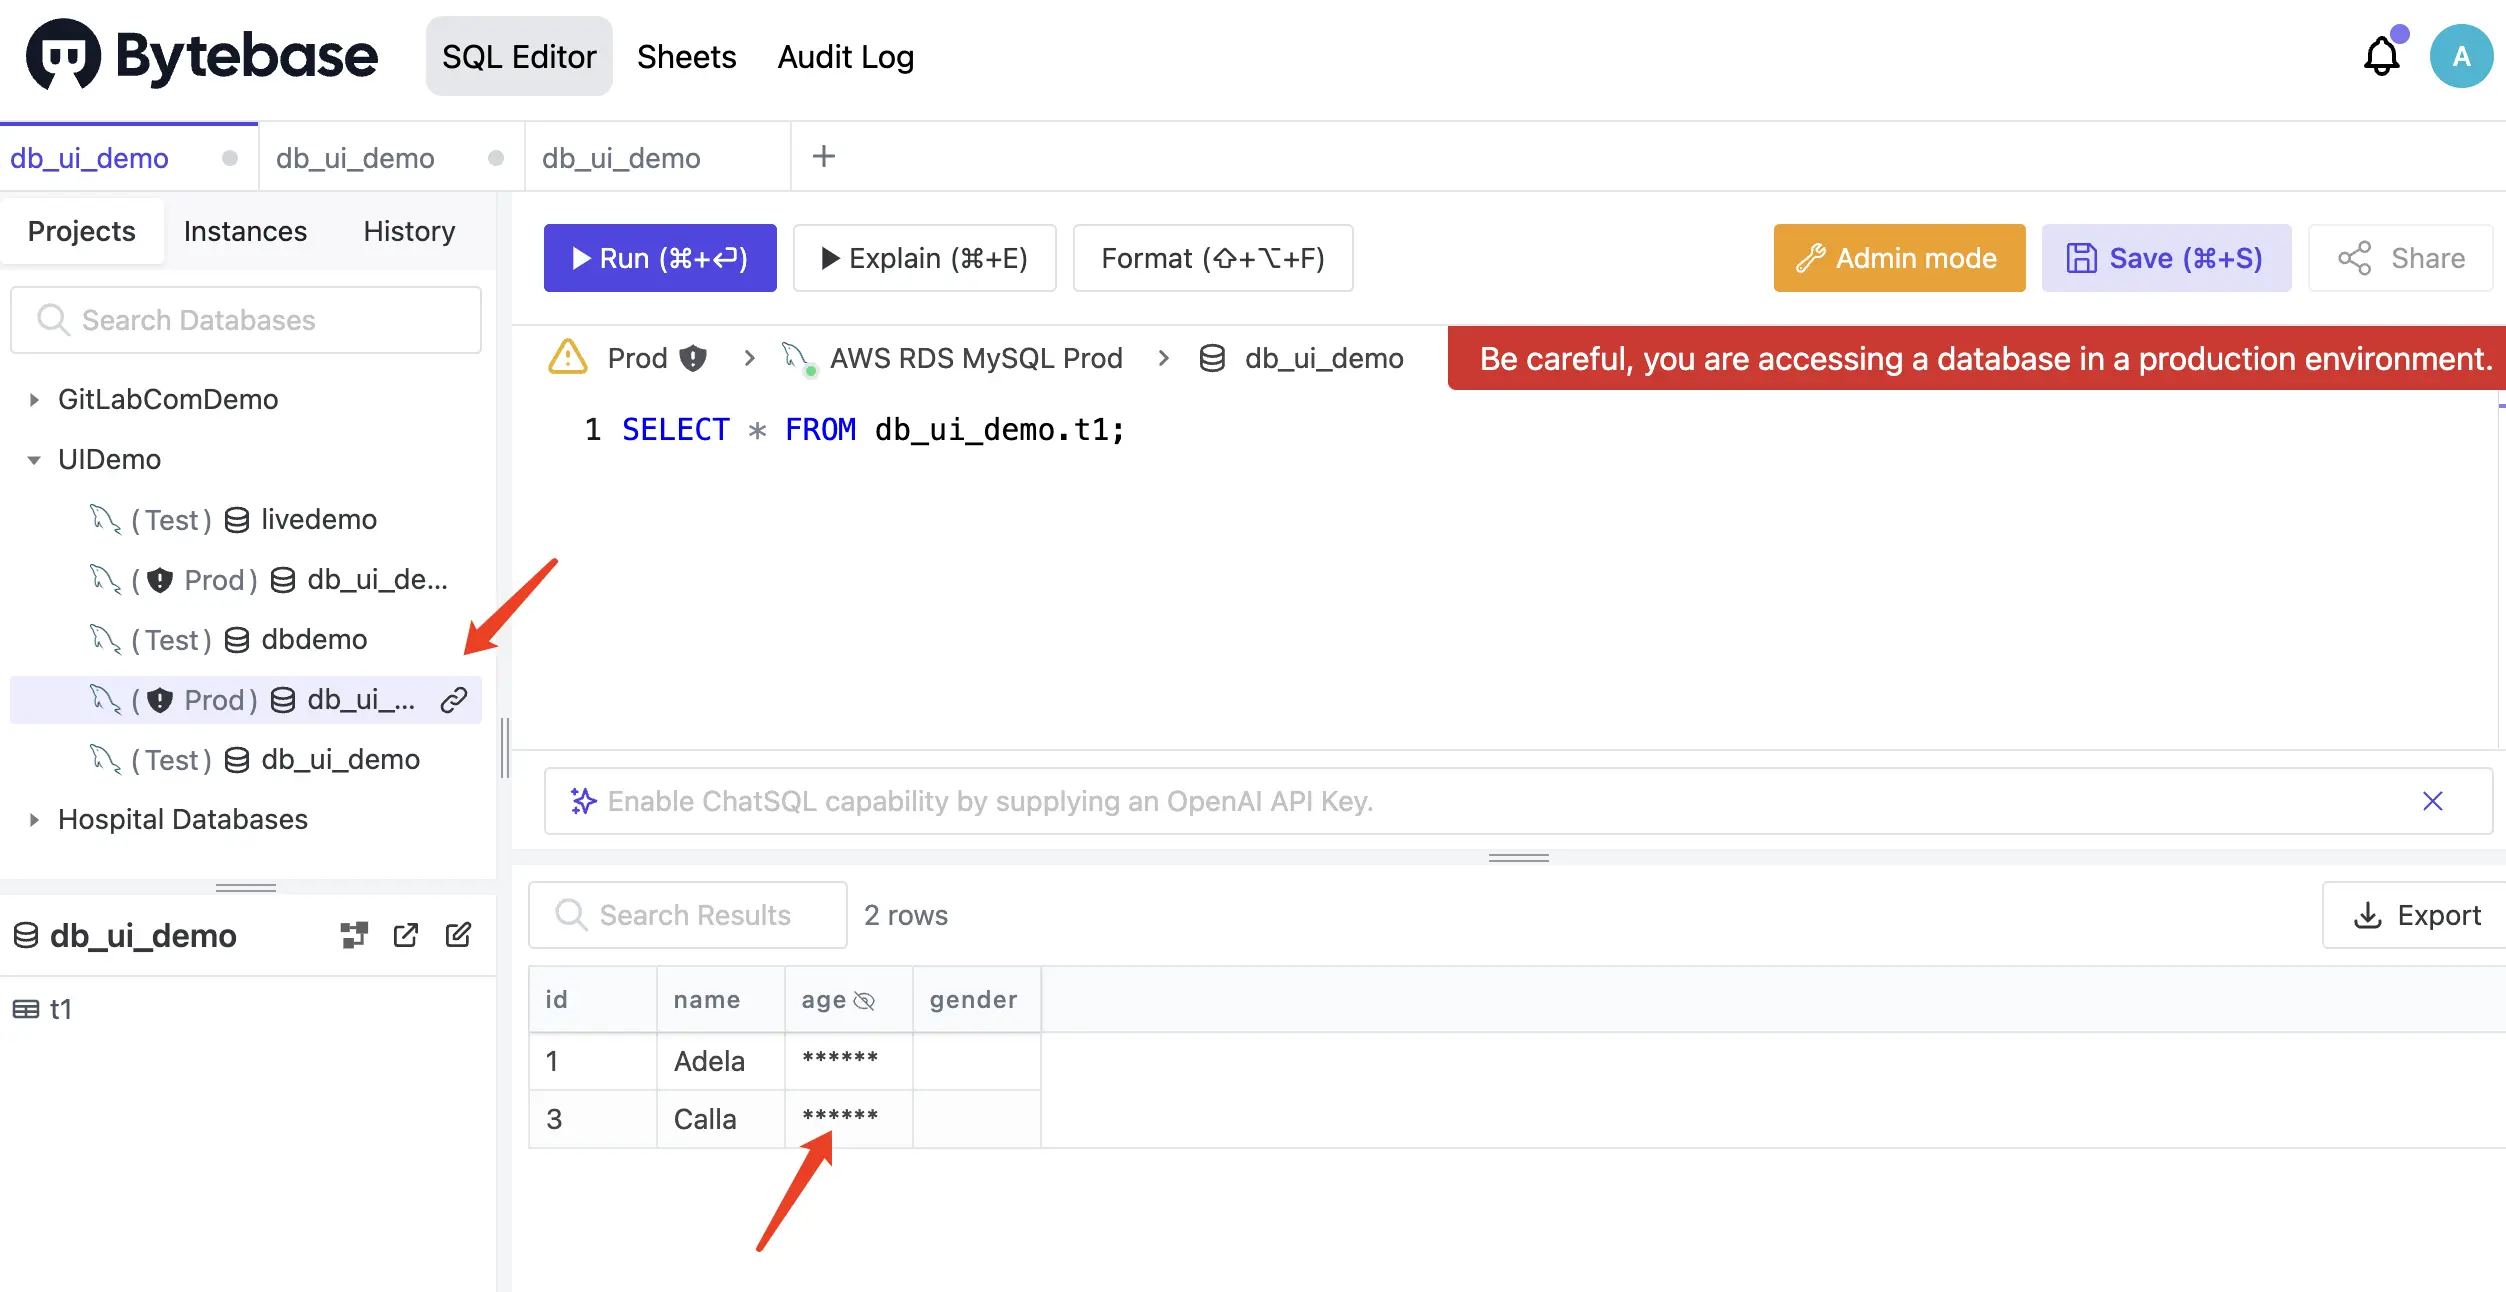 Bytebase SQL Editor with controlled data access
Security and Compliance
Both vendors sell to teams facing SOC 2, SOX, PCI DSS, or HIPAA audits, and both publish compliance guides. They cover different parts of what an auditor asks for. Liquibase Secure governs the change pipeline. Bytebase governs the change pipeline and access to the data itself.
| Control an auditor asks about | Liquibase | Bytebase |
|---|---|---|
| Checks before a change deploys | Secure: policy checks on changelogs, SQL, and the live database, including a personal-data check; CI blocks on exit code. Community: none | SQL Review: 200+ engine-specific rules on every tier, configured per environment |
| Who authorizes a production change | Outside the product: CI/CD gates, SSO, and change-management tools | Enterprise: risk-based approval flows attached to the change. All tiers: per-environment rollout permissions |
| Who can query or export production data | Out of scope | Roles and the SQL Editor on all tiers; Enterprise: just-in-time access that expires, and dynamic data masking |
| Credentials for deployments | Secure: HashiCorp Vault and AWS Secrets Manager extensions | Enterprise: external secret managers (HashiCorp Vault, AWS Secrets Manager, GCP Secret Manager) for database passwords; users and agents act through their Bytebase identity, not shared credentials |
| Audit evidence | Community: DATABASECHANGELOG. Secure: structured JSON logs to a SIEM, plus update, rollback, drift, and checks reports. Change Intelligence, a central audit view, is in private preview | Audit log of changes and data operations (Pro: 7 days; Enterprise: no limit), exportable through the API |
| Drift detection | Secure: monitoring, alerts, and drift reports | Not offered (removed in 3.14); schema sync restores a known version |
| AI agents changing the database | Secure 5.2 routes AI- and MCP-authored schema changes through the same checks and audit | MCP server acts with the user's permissions; query results are masked and every action is audit-logged |
How that plays out depends on the audit scope.
If the scope is change management, the SOX change-management controls or SOC 2 CC8.1, both tools can produce evidence. With Liquibase Secure, the evidence is assembled from your CI system's approvals, the policy-check results, and logs in your SIEM. With Bytebase, the review result, the approval, and the rollout record sit on the same change.
If the scope also covers access to production data, such as SOC 2 CC6, PCI DSS Requirements 7 and 10, or HIPAA's access and audit controls, Liquibase covers none of it by design, and you would add a separate access or PAM tool. Bytebase covers query access, masking, temporary grants, and the audit trail for them in the same product.
Liquibase Secure is ahead in two places: checks that scan the live database and flag personal data inside migration SQL, and drift detection. If direct DDL access to production cannot be removed, drift reports matter more than prevention.
Pricing
Liquibase restructured its pricing in September 2025 into five tiers: Community (free), Starter, Growth, Business, and Enterprise. All paid tiers are branded "Liquibase Secure." Paid plans are gated by number of applications, database types, and company revenue (Starter and Growth require under $1B revenue). No public pricing — quotes only.
Bytebase has three tiers: Community (free, self-hosted, with user and instance limits), Pro (per-user, on Bytebase Cloud), and Enterprise (custom annual pricing, self-hosted, with Cloud Enterprise coming soon). Pro pricing is public; see the pricing page for current numbers.
When to Choose Liquibase
- Your team is CLI-first and wants to embed migrations directly into existing CI/CD pipelines.
- You need to support a wide range of databases (60+), including niche or legacy systems.
- Your developers already work in Java/JVM ecosystems.
- You need a migration engine, not a governance platform — access control and approval happen in other tools.
- You want policy checks that scan the live database and flag personal data in migration SQL, plus drift detection, and production data access is already governed by another tool.
When to Choose Bytebase
- You want an all-in-one platform that covers migration, SQL review, access control, data masking, and audit logging — not just a migration CLI.
- Your team includes DBAs or platform engineers who review database changes before they reach production.
- You need compliance evidence that covers both database changes and access to production data — approval flows, just-in-time access, data masking, and one audit trail for SOC 2, PCI DSS, HIPAA, GDPR, or internal security policies.
- You're running multi-environment or multi-tenant deployments where batch change orchestration matters.
- You want to declare a target schema and have the migration generated for you, on PostgreSQL or MySQL, without giving up review and approval on the generated DDL.
FAQ
Which is better for security and compliance, Liquibase or Bytebase?
It depends on what your audit covers. For change management alone, both work: Liquibase Secure adds policy checks, drift detection, vault integrations, and structured logs, with approvals handled in your CI/CD system. Bytebase attaches SQL review (every tier) and risk-based approval (Enterprise) to the change itself. If the audit also covers who can read or export production data, Liquibase stays out of that layer by design, while Bytebase adds role-based query access, just-in-time grants, data masking, and an audit log of data operations. See Security and Compliance for the control-by-control view.
Can I use Liquibase and Bytebase together?
They solve different layers. Liquibase handles the migration file format and execution; Bytebase handles collaboration, review, and governance. Most teams pick one, but if you already have a library of Liquibase changelogs, you don't have to throw them away — Bytebase can manage the review and deployment side while Liquibase stays as the execution engine.
Is Liquibase still open source?
Liquibase Community switched from Apache 2.0 to the Functional Source License (FSL) in September 2025. FSL is not an OSI-approved open source license — it restricts commercial use in competing products. Each version reverts to Apache 2.0 after two years. Bytebase is MIT licensed, with enterprise features under a commercial license.
Which tool has better CI/CD integration?
Depends on what "CI/CD integration" means to you. If it means "I want a command I can add to my Jenkins/GitHub Actions pipeline," Liquibase wins — it's just a CLI call. If it means "I want SQL in a pull request to get engine-specific review as a required check, then roll out across environments with a record in Bytebase," Bytebase's GitOps integration does that out of the box.
What happened to Liquibase Hub?
Liquibase Hub (the web dashboard) was sunset in April 2023 and never replaced. There's no Liquibase GUI anymore. The Secure edition compensates with structured JSON logs you can pipe into Datadog or Splunk, and a VS Code extension for IDE-based interaction — but if you want a web UI for database changes, Liquibase doesn't have one.